Reflex
Reflex is the automated response of SenseOn against Ransomware threats. These threats often spread too quickly for manual human intervention. Reflex uses multiple detection techniques. It can automatically and rapidly isolate one or more endpoints, and it quarantines malicious activity and stops the spread of Ransomware strains. SenseOn Reflex operates 24/7 and continuously responds to threats. It stops the progress of attacks before they become a problem. It helps to prevent lateral spread across the network, and it limits possible damage.
The SenseOn case that follows is an example. It shows how Reflex detects and intervenes in a ransomware infection chain.

How Reflex Works
When there is proof of ransomware activity, Reflex makes sure that the device is isolated from the network. The isolation blocks all non-essential communication, and this prevents more spread. Only the connectivity with the SenseOn platform stays active, so that response actions are possible. You can configure Reflex in one of two modes:
- Automatic: Reflex isolates the device immediately after detection.
- Manual Approval: Reflex sends an alert to approve or deny the device isolation. This mode gives more control, and confidence stays high, because Reflex reported zero false positives up to now.
Reflex Configuration
Configure Reflex to isolate devices automatically or to make manual approval from an authorised user necessary. To do this, first create segments. The segments define the configuration for specified devices.
Segment creation: To create a segment, go to
Settings>Device Configuration>Create a new Segment
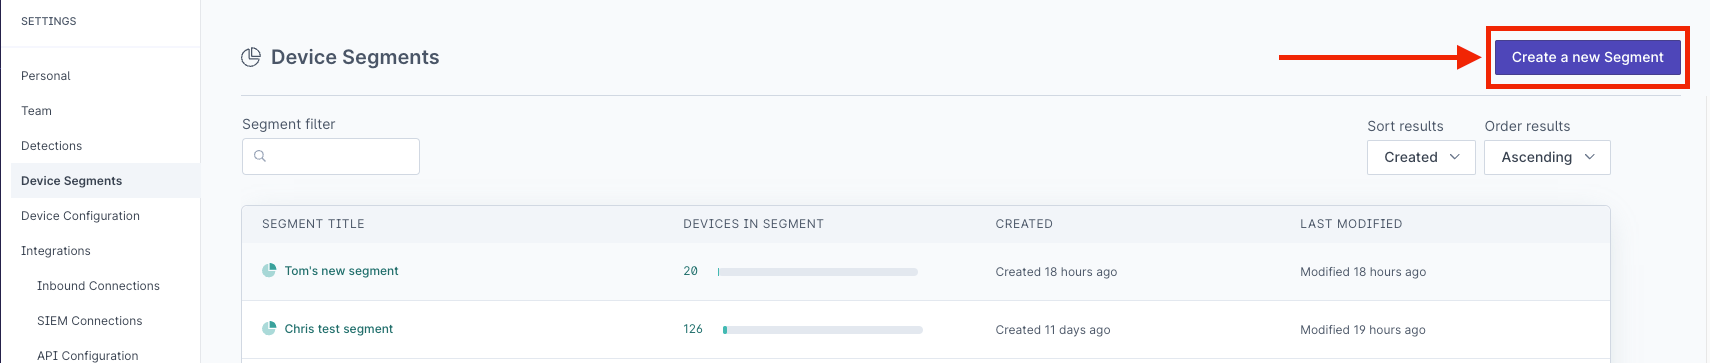
After you create the segment for the Reflex configuration, select the option to edit the configuration of that segment.
Device Configuration. Select the segment that you want to apply the settings to. To change a setting, clickedit.

Under Reflex, select the configuration that you want for Reflex in that device segment.

Key Benefits
| Benefit | Description |
|---|---|
| Early Ransomware Detection | Finds and responds to aggressive ransomware activity before it can spread. |
| Stops Lateral Movement | Immediately isolates affected devices. This prevents spread to other endpoints. |
| Zero False Positives | Reflex showed high accuracy. As a result, it is less necessary for administrators to do checks of its actions. |
| Operational Flexibility | Supports automatic and manual containment modes. Each customer selects the mode that it prefers. |
| Low-Impact Integration | Runs in the background with minimal impact on normal operations or device performance. |
Use Cases
Reflex is especially useful in environments where: - Ransomware is a high-priority threat. - Fast containment is critical to business continuity. - SOC teams must have confidence in automated response. - Security operations want to minimise manual work.
Who Should Use Reflex?
Reflex is ideal for: - Security Operations Centres (SOCs) that want to decrease the incident response time. - CISOs and IT Leaders who want assurance against ransomware outbreaks. - Incident Responders who want tools that limit the impact without manual intervention.